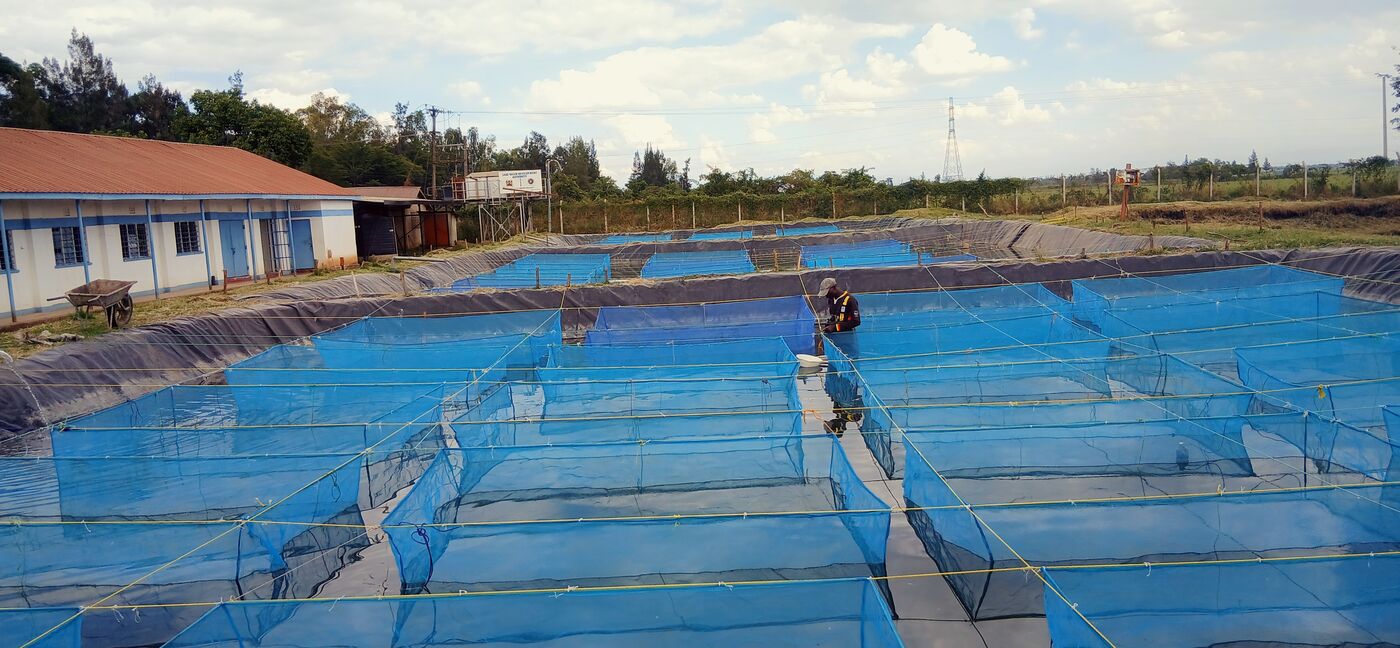
A lot of IoT system designs quietly assume the network connection is always there, and the code only really gets tested against that assumption. Around Lake Victoria, cellular connectivity is good most of the time but not continuous: weather, network congestion, carrier maintenance, and simple signal shadowing from terrain or vegetation all cause real, if intermittent, drops. A system that only works when connectivity is perfect isn't actually field-ready, no matter how well it performs on a demo day.
The core idea: the node should never depend on the network to do its job
Offline-first design starts from a simple principle: the device's core function (sensing, deciding, and acting locally where it can) should not depend on network connectivity being present at that moment. Connectivity is for getting data out and commands in when it's available, not a prerequisite for the device doing anything useful at all.
For a water quality monitoring node, this means the node itself should be able to detect a dangerous dissolved oxygen reading and trigger a local response (an audible alarm, a local relay controlling an aerator) without needing to reach a cloud service first to make that decision. The network is for reporting what happened and enabling remote visibility, not for the critical real-time decision itself.
Local buffering: don't lose data during a gap
When connectivity drops, a node with no local storage simply loses every reading taken during that gap. A node designed offline-first buffers readings locally (to onboard flash storage, an SD card, or similar) and continues logging normally regardless of whether it can currently reach the network.
This matters more than it might seem: a gap in your data record during exactly the period when connectivity was unreliable is often also a period of unusual weather or conditions, which correlates uncomfortably well with the events you most want visibility into, like the upwelling conditions we covered in an earlier post.
Store-and-forward: sync when the network comes back
Once connectivity returns, a properly designed node should automatically detect this and sync its buffered data, in order, filling the gap in the historical record rather than only reporting from the moment connectivity resumed. This is usually implemented as a simple queue: readings are appended locally with a timestamp, and a background process attempts to drain that queue to the server whenever a connection is available, resuming cleanly if it's interrupted mid-sync.
This is a modest amount of additional firmware complexity compared to a naive "just try to send every reading immediately" design, but it's the difference between a complete historical record and a record full of unexplained gaps exactly when things were going wrong.
Local alerting as a first line, remote alerting as a second
For anything time-critical, like an oxygen threshold alert, a fully offline-first design treats the node's own local alert (a loud buzzer, a visible light, a direct relay action) as the first line of defence, one that works with zero dependency on connectivity at all. The SMS or app notification to a farmer's phone is a valuable second layer, but it should never be the only mechanism, because it is exactly the layer most likely to be affected by the same conditions (a storm knocking out cellular coverage) that might also be causing the underlying problem.
Designing the sync protocol to be resumable
A subtler failure mode: a sync process that isn't designed to be safely interrupted can leave data in an inconsistent state if connectivity drops mid-transfer, sometimes worse than not attempting the sync at all (duplicate records, or records marked as sent when they weren't). A resumable protocol, acknowledging each record only once the server confirms receipt and only then removing it from the local queue, avoids this regardless of how or when the connection happens to drop.
What this costs, and what it buys
Offline-first design adds real engineering effort: local storage management, a queue and sync protocol, and local decision logic that has to work without checking in anywhere. What it buys is a system that keeps doing its actual job (measuring, deciding, alerting locally) through exactly the conditions, storms, network congestion, remote terrain, where a naive always-connected design fails silently and leaves you with a gap in the record at the worst possible time.
If you're designing or reviewing an IoT system for a site with less-than-perfect connectivity and want to make sure it's genuinely offline-first rather than just optimistic, get in touch. You can also see how we take hardware from prototype to the field.